Key Highlights
- The difference between a data controller and a data processor
- The main GDPR responsibilities assigned to each role
- How joint controllers and sub-processors fit into data processing
- When an organization must appoint a Data Protection Officer
- The seven GDPR principles that guide personal data use
- Practical steps your organization can take to support compliance
Editor's Note: This post was originally published in March 2018 and has been updated with additional content in October 2026.
One of the much-discussed elements of the GDPR law is the new guidelines it has laid down for data controllers and processors. While the GDPR retains some of the obligations that the Data Protection Directive places on both parties, it has introduced some new ones too. In this blog, we will discuss the data processor and controller responsibilities that the GDPR has conferred on each and provide insights into how an organization, whether it is a controller or a processor, can start preparing itself to be GDPR-ready.
Who is a Data Controller?
In today’s digital world, data collection and storage are more of a norm than an exception. Businesses may collect individual data for advertising, marketing, analytical, or research purposes. Each time a business collects and processes an individual’s personal data, it does so as a ‘controller’ or a ‘processor.’ A data controller is defined in Chapter 1, Article 4:
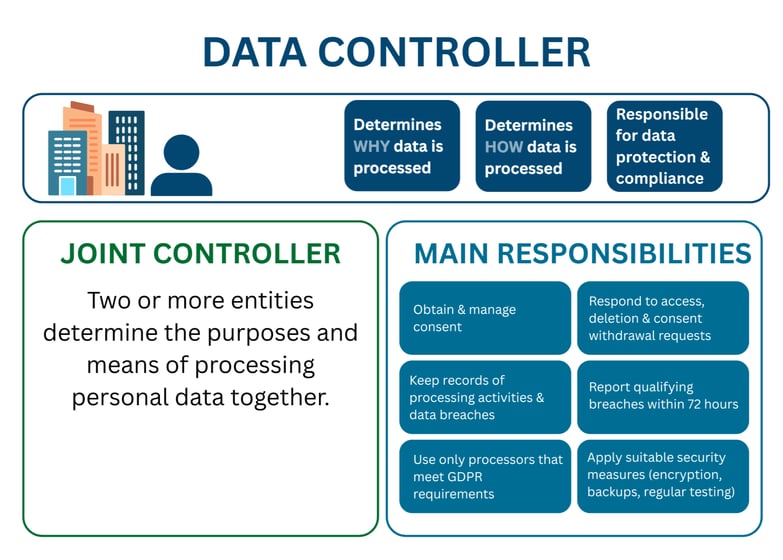
‘Controller’ is “the natural or legal person, public authority, agency or other body which, alone or jointly with others, determines the purposes and means of the processing of personal data.”
An organization that makes decisions about personal data is a data controller.
|
Your organization is likely a data controller if it decides:
|
What is a Joint Controller?
A joint data controller refers to two or more entities determining the purposes and means of processing personal data together. Unlike a standard data controller, which independently decides how to handle data, joint controllers share responsibility and must clearly define their respective roles and obligations.
For example:
A bank and an insurance company jointly develop a financial product and decide how customer data will be processed. Since they both influence the data processing decisions, they are considered joint controllers under the GDPR (General Data Protection Regulation).
|
Joint controllers must agree on their respective responsibilities. They should also explain these arrangements to data subjects and provide a clear point of contact for privacy requests. |
What is the Main Responsibility of a Data Controller?
A data controller decides why and how personal data is collected and used. It is responsible for protecting that data, respecting individuals’ rights, and proving compliance with the GDPR.
Key responsibilities include:
- Obtaining and managing consent
- Responding to access, deletion, and consent withdrawal requests
- Keeping records of processing activities and data breaches
- Reporting qualifying breaches within 72 hours
- Using only processors that meet GDPR requirements
- Applying suitable security measures, such as encryption, backups, and regular testing
When consent is withdrawn, the controller must ensure the relevant data is removed, including data held by processors.
Where two or more organizations jointly control personal data, they must clearly define their responsibilities and provide individuals with a clear point of contact. Joint controllers may be held fully liable for GDPR failures.
The GDPR does not provide a general exemption for force majeure or unforeseen events. Controllers may still carry the legal and financial risk if compliance obligations are not met.
What is the Definition of a Data Processor?
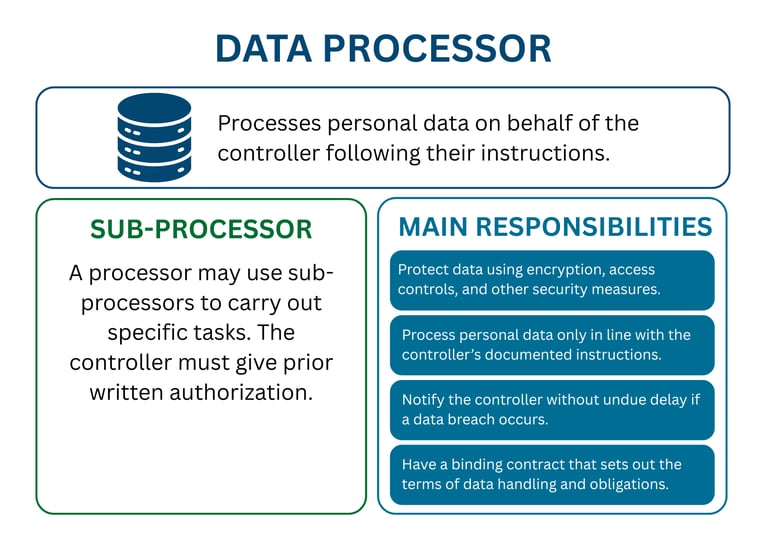
"A data processor is defined under the GDPR as "a natural or legal person, public authority, agency or other body which processes personal data on behalf of the controller.”
If an organization holds or manages the data but does not decide how or why that data is used, it acts as a processor. The processor is a third-party entity carrying out instructions from the controller.
The data processors must process information only as directed, and they are not allowed to make decisions regarding the purpose of processing without explicit authorization from the data controller. They are required to implement measures to ensure data protection, maintain processing records, and notify the controller in the event of a breach. This role is subject to strict responsibilities under the GDPR, and a binding contract must govern the relationship with the controller.
|
Does your organization decide why the data is processed? |
What is a Sub-Processor?
A sub-processor must be authorized by the controller. A processor is a third-party entity that handles data on the controller’s behalf, and it may work with sub-processors to fulfill its responsibilities. The controller must provide prior written authorization before the processor engages any sub-processor.
For example:
A cloud hosting provider hired by an email marketing platform to store and process customer email data is a sub-processor. The email marketing platform is the processor, while the business using the platform is the data controller.
|
A processor should not appoint a sub-processor without the controller’s prior written authorization. The processor also remains responsible for ensuring the sub-processor meets its data protection obligations. |
Data Processor Duties
A data processor is responsible for handling personal data only as instructed by the data controller and must comply with data protection laws. Key responsibilities include:
- Ensuring data security through encryption and access controls.
- Processing data lawfully and in line with the controller’s instructions.
- Informing the controller of data breaches.
- Signing a Data Processing Agreement (DPA) that outlines the terms of data handling.
A processor does not determine why or how personal data is collected but ensures compliance with the controller’s directives.
Example of a Data Controller and Data Processor
Scenario: Online Retail Store and Payment Processor
A fashion e-commerce company (ShopTrend) sells clothing and accessories online. To process payments securely, it integrates with PayFast, a third-party payment processing service.
- Data Collection:
- A customer visits ShopTrend’s website and places an order.
- During checkout, the customer enters their name, billing address, shipping address, and payment details.
- Who is the Data Controller?
- ShopTrend determines why and how customer data is collected (e.g., for order processing, fraud prevention, and customer service).
- Since ShopTrend makes the decisions regarding data collection and storage, it is the data controller.
- Who is the Data Processor?
- PayFast processes the payment details (credit card number, expiration date, CVV, etc.) on behalf of ShopTrend.
- PayFast follows ShopTrend’s instructions and only processes payments—it does not decide how the data is used beyond this purpose.
- Because PayFast acts under ShopTrend’s instructions, it is a data processor.
- Key Responsibilities:
- ShopTrend (Controller) must ensure customer data is collected lawfully, inform users about its privacy policy, and handle requests like data deletion or access requests.
- PayFast (Processor) must ensure that customer payment information is secure, comply with GDPR and PCI DSS (Payment Card Industry Data Security Standard), and report any data breaches to ShopTrend.
Data Processor vs Controller: Who Does What
The processor is forbidden from using personal data it is entrusted with for purposes other than the ones outlined by the data controller. Upon request, the processor has to delete or return all personal data to the controller at the end of the service contract.
|
The GDPR places direct obligations on controllers and processors. Penalties may depend on each party’s responsibilities, conduct, and security measures. |
Data Controller vs. Data Processor: Who is Impacted by the GDPR?
The answer to this is both. Under the outgoing Data Protection Directive 95/46/EC, only controllers are liable for data protection noncompliance. However, the EU General Data Protection Regulation (GDPR) will strike a balance by allotting direct obligations to data processors.
According to Article 83, in the case of non-compliance, fines can be applied to both controllers and processors. These fines shall be imposed regarding “the degree of responsibility of the controller or processor taking into account technical and organizational measures implemented by them.”
This represents a significant change and will dramatically increase the risk profile for entities like cloud and data center providers that act as data processors. However, the impact will also be felt by controllers who engage their services, as the increased cost of compliance may lead to a consequent increase in the cost of the processors’ services. Controllers will also have to be extra vigilant about the processors they engage with and ensure they have the technical and operational measures required to be GDPR-compliant.
What Will a Data Processor Have to Do to be GDPR Compliant?
The processor is forbidden from using personal data it is entrusted with for purposes other than the ones outlined by the data controller. Upon request, the processor has to delete or return all personal data to the controller at the end of the service contract.
It can transfer personal data to a third country only after it receives legal authorization.
It has to obtain written permission from the controller before engaging a subcontractor and assume full liability for failures of subcontractors to meet the GDPR.
The processor has to enable and contribute to compliance audits conducted by the controller or a controller representative.
If there is a data breach, the processor is expected to notify the data controllers without undue delay
A processor is further required to maintain a record of data processing activities if it qualifies for any of the following criteria:
- Employs 250 or more persons
- Processes data that is “likely to result in a risk to the rights and freedoms of data subjects.”
- Processes data more than occasionally.
- Processes special categories of data as outlined in Article 9(1)
- Processes data relating to criminal convictions
Processors must also review existing data processing agreements to ensure they have met their compliance obligations under the GDPR.
Detailed Responsibilities Under GDPR: Controller vs Processor
Regarding GDPR, understanding the responsibilities of a data processor and a data controller is crucial. The GDPR Controller, often an organization or business, determines the purposes and means of processing personal data. On the other hand, the Processor processes data on behalf of the controller, often a third-party company providing a specific service.
Data Processor Responsibilities Under GDPR
The data processor's responsibilities are defined primarily by the controller. Still, they can include tasks like data collection, recording, organization, structuring, storage, alteration, retrieval, consultation, use, disclosure by transmission, dissemination, or otherwise making available, alignment or combination, restriction, erasure, or destruction. These responsibilities should be outlined in a signed agreement between the Controller and Processor.
The GDPR mandates processors to maintain records of their processing activities and to implement appropriate security measures. Additionally, processors are required to appoint a Data Protection Officer (DPO) if they carry out large-scale processing of special categories of data. If a data breach occurs, it's the processor's responsibility to notify the controller without undue delay.
Controller Responsibilities Under GDPR
The GDPR Controller decides why personal data needs to be processed and how it will be processed. As a controller under the GDPR, an entity must ensure that all data processing activities comply with the GDPR's principles. These principles include lawfulness, fairness, transparency, purpose limitation, data minimization, accuracy, storage limitation, and integrity and confidentiality.
GDPR Controllers must demonstrate compliance with these principles and could be held liable for any breaches. To prove compliance, controllers should keep records of their processing activities, conduct data protection impact assessments for high-risk processing activities, and ensure the implementation of proper security measures.
In summary, the key difference between the controller's GDPR and the processor controller is that the GDPR Controller is responsible for ensuring overall compliance with data protection laws. At the same time, the Processor acts under the instruction of the Controller.
It's important to remember that although their responsibilities differ, both the data controller and processor must work together to ensure GDPR compliance. Clear communication and defined roles can help each party meet its obligations effectively.
Who is Required to Appoint a DPO?
GDPR mandates the appointment of a DPO for organizations, irrespective of size or role as a data controller or data processor, in select circumstances outlined in the GDPR definition of processing personal data.
Under the GDPR (Article 37), there are three main scenarios where the appointment of a DPO by a data controller or data processor is mandatory:
- A public authority carries out the processing.
- The core activities of the controller or processor consist of processing operations that require regular and systematic processing of data subjects on a large scale; or
- The core activities of the controller or processor consist of processing large-scale sensitive data or data relating to criminal convictions/offenses.
Core activities here refer to a controller or processor’s key operational activities. This does not include supporting activities such as payroll or IT support, which are ancillary functions.
Organizations consider several factors when determining if their processing is of a ‘large scale.’ These include:
a) the number of data subjects concerned;
b) the volume of data or range of data items;
c) the duration of the processing; and
d) the geographical extent of the process.
Regular and systematic monitoring includes all forms of tracking and profiling on the internet. It is, however, not restricted to the online environment and could also have offline activity. ‘Regular’ monitoring will mean ongoing or occurring at particular intervals for a specific period, recurring or repeated at fixed times, or constantly or periodically taking place. ‘Systematic’ monitoring refers to monitoring that happens according to a system, pre-arranged, organized, or methodical, taking place as part of a general plan for data collection, or carried out as part of a strategy.
It is also important to note that if an organization does not meet the requirements of the GDPR, it may instead voluntarily decide to appoint a DPO. The exact requirements that apply to mandatory DPOs will still apply. Therefore, if an organization chooses not to appoint a DPO, it is advised to document those reasons.
Qualifications of a GDPR Officer
While the GDPR does not specify their precise credentials, a data protection officer must have enough professional experience and knowledge of data protection law. This expertise should be proportionate to the type of processing the organization carries out and the level of protection the personal data requires.
Disclaimer: Please note that in this blog, we have provided basic information regarding the GDPR. WSI is not a legal authority for GDPR and can only offer advice on the best practices to follow while carrying out any digital marketing initiative. However, for advice regarding the legal interpretation of this law for your business, please approach a legal or data protection official.
What Are the 7 Principles of the General Data Protection Regulation (GDPR)?
The way organizations collect, store, and use personal data is governed by the rules and regulations of the GDPR. The guidelines stipulated by the GDPR include:
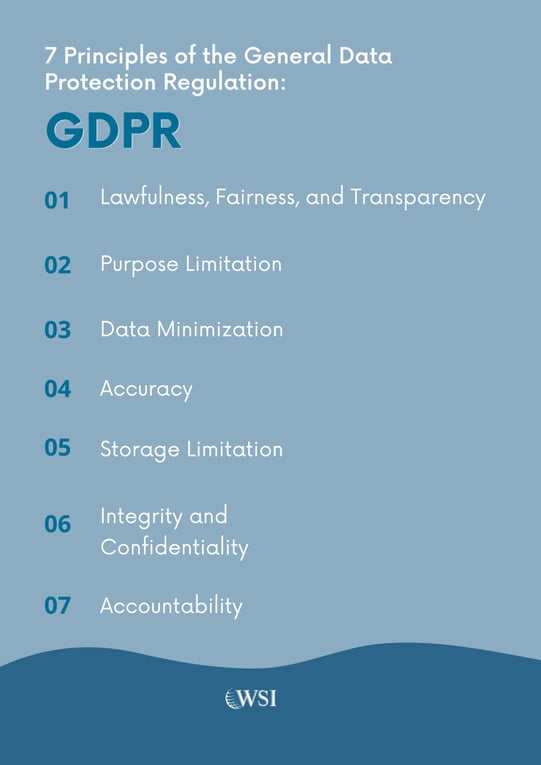
1. Lawfulness, Fairness, and Transparency
Full transparency about the disclosure of how data is used is compulsory for all organizations in the UK. Should a data subject request more information about how their data is stored, used, and distributed, it has to be disclosed to them within a specified time frame as stipulated by the GDPR.
2. Purpose Limitation
Organizations must state the reasons they are using the data subject's information. It can only be used, stored, and processed for this purpose, and this purpose only, unless otherwise stipulated and agreed to by the data subject. This is not, however, strictly applied to information gathered for scientific, statistical, or historical purposes.
3. Data Minimization
As the name suggests, only data required for the purposes for which it was collected should be used. In other words, data collected should not just be stored for a ‘just in case' scenario. It should be used as and when it is needed according to the organization's requirements. Any additional information that is kept over and above this is considered unlawful.
4. Accuracy
Accuracy of information is paramount to complying with the regulations as stipulated by the GDPR. Data subjects also hold the right to request that incorrect information be deleted within 30 days if their information is incorrect, incomplete, or outdated.
5. Storage Limitation
Data should only be stored as long as the organization needs the information for its intended use. There should be a framework in place for review purposes to ensure that outdated information is purged from the system. This does not apply to data stored for historical or statistical purposes.
6. Integrity and Confidentiality
Organizations must ensure that the data subject's personal information is always protected. This gives credence to the organization’s ability to handle personal data with integrity. It provides the data subjects peace of mind that their personal information won't be exposed online or interfered with by hackers who use malware and phishing methods to obtain data illegally.
7. Accountability
Accountability precedes transparency. This means that organizations must show that they have taken the necessary steps and followed the guidelines stipulated by the GDPR to ensure that they exhibit the principle of transparency.
Some of these data handling guidelines include implementing and evaluating the guidelines of the GDPR, appointing a supervisor in charge of data protection, and ensuring that the required consent is obtained at all times for data processing purposes.
| Process personal data lawfully, use it for a clear purpose, collect only what you need, keep it accurate, delete it when it is no longer required, protect it, and keep evidence of compliance. |
Where Are We Now?
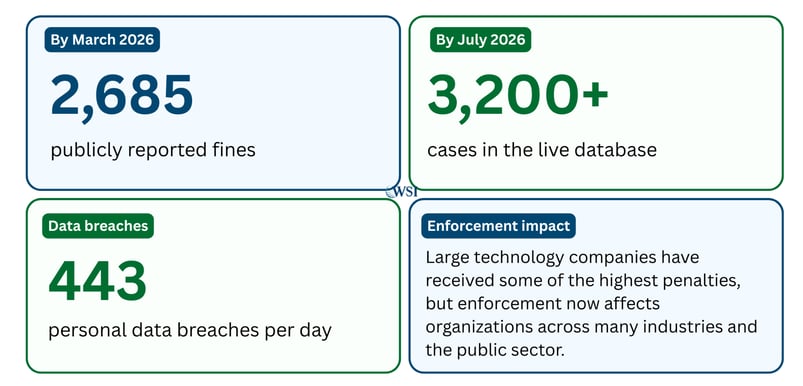
Where are we now in practical terms concerning the GDPR? Key issues surrounding the complexity of the GDPR are still being debated. Since coming into effect, there have been over 900 GDPR-related fines and cases across the UK alone. The number should give us some valuable insight into compliance with the law and the issues involved with how the GDPR is being enforced.
By March 2026, the CMS GDPR Enforcement Tracker had recorded 2,685 publicly reported fines worth approximately €6.11 billion. Its live database showed more than 3,200 cases and €6.31 billion in fines by July 2026. European organizations also reported an average of 443 personal data breaches per day between January 2025 and January 2026, a 22% annual increase. Large technology companies have received some of the highest penalties, but enforcement now affects organizations across many industries and the public sector. Some major fines remain under appeal, so reported totals and final penalty amounts may change.
The countries most affected by GDPR compliance issues include Italy, Spain, Luxembourg, and Ireland. Fines range from high-value to low-value fines. Although we are unsure what drives compliance in some countries, a common theme is high-value fines for high-value companies. As we saw from the above data, larger companies will often see larger data breaches and, as a result, incur heavier fines.
Where Are We Heading?
Data protection is becoming more global, with organizations held accountable for how they manage personal data, regardless of where they operate.
GDPR enforcement increasingly involves cooperation between national regulators. Cross-border complaints are usually handled by the authority in the country where the organization has its main EU establishment, while other affected authorities may take part.
Future priorities include:
- Stronger security requirements for controllers and processors
- Regular testing and review of data protection measures
- Clearer rules on liability when a processor causes a breach
- Continued oversight of international data transfers
- Greater accountability across suppliers and service providers
The EU and the US have also continued to refine rules for transferring personal data. Organizations must ensure that international transfers have suitable legal and security protections.
Data protection is an ongoing business responsibility. Companies must regularly review their processes, suppliers, security controls, and legal obligations.
Does It Still Apply?
Today, data protection is still a work in progress. It is deemed a long-term process and a project that affects all businesses and the economy. In the EU, GDPR no longer applies to the UK. If you are outside the UK, your business must comply with the Data Protection Act 2018. The EU GDPR was incorporated into this law.
Although the law has changed, nothing has been affected concerning data protection rights and obligations that companies must follow. GDPR policies are used today to ensure compliance and understanding of the principles and obligations of data protection.
It is essential to note that the EU GDPR may still apply if you operate in the EEA. You may have to follow the regulations if you offer services to individuals or companies in the EEA. It is best to check with applicable government officials to see which law applies to your business.
How Can I Ensure Compliance?
Although the GDPR lists the results it expects from companies that comply with good data management, it does not describe the steps companies should take to ensure GDPR compliance. Here are some tips we compiled to help you meet your data protection responsibilities and goals.
- Always ask for compliance or permission from participants before collecting personal data.
- Remember, you will be responsible for whether you use the information from the collected data or not. Collect data that is required of you and only what is required of you. If you are unsure whether to collect specific data, you should put your data collection on hold.
- Collect permission from participants if you need to share their information outside your entity. Without permission, do not share the data you collected with entities other than your company.
- All data should be encrypted for user protection.
- Keep data secure by backing up all data and keeping it in a secure off-site location.
- Ensure you use the correct tools to edit and delete data when needed.
Prepare Your Organization for GDPR Compliance
The GDPR will affect organizations in many ways beyond data security and policies. Businesses that will be impacted must seek help or legal counsel if required. At the very least, they need a clear plan of action that includes training on GDPR, revisiting their data flow and processing mechanisms, reviewing their privacy practices and policies, leveraging third-party data, and more.
To get started on becoming GDPR data processing ready, we invite you to download our “12-Point Checklist to Help Prepare Your Organisation for GDPR” by clicking here. This checklist covers essential steps for both data processors and controllers, helping your organization ensure compliance with GDPR and safeguard personal data. For additional information, please do not hesitate to speak to an expert at WSI!
Sources:
General Data Protection Regulation - GDPR
Guide to the UK General Data Protection Regulation (UK GDPR)
Chapter 10: Obligations of Controllers – Unlocking the EU General Data Protection Regulation
GDPR: Where are we now? And where are we going?